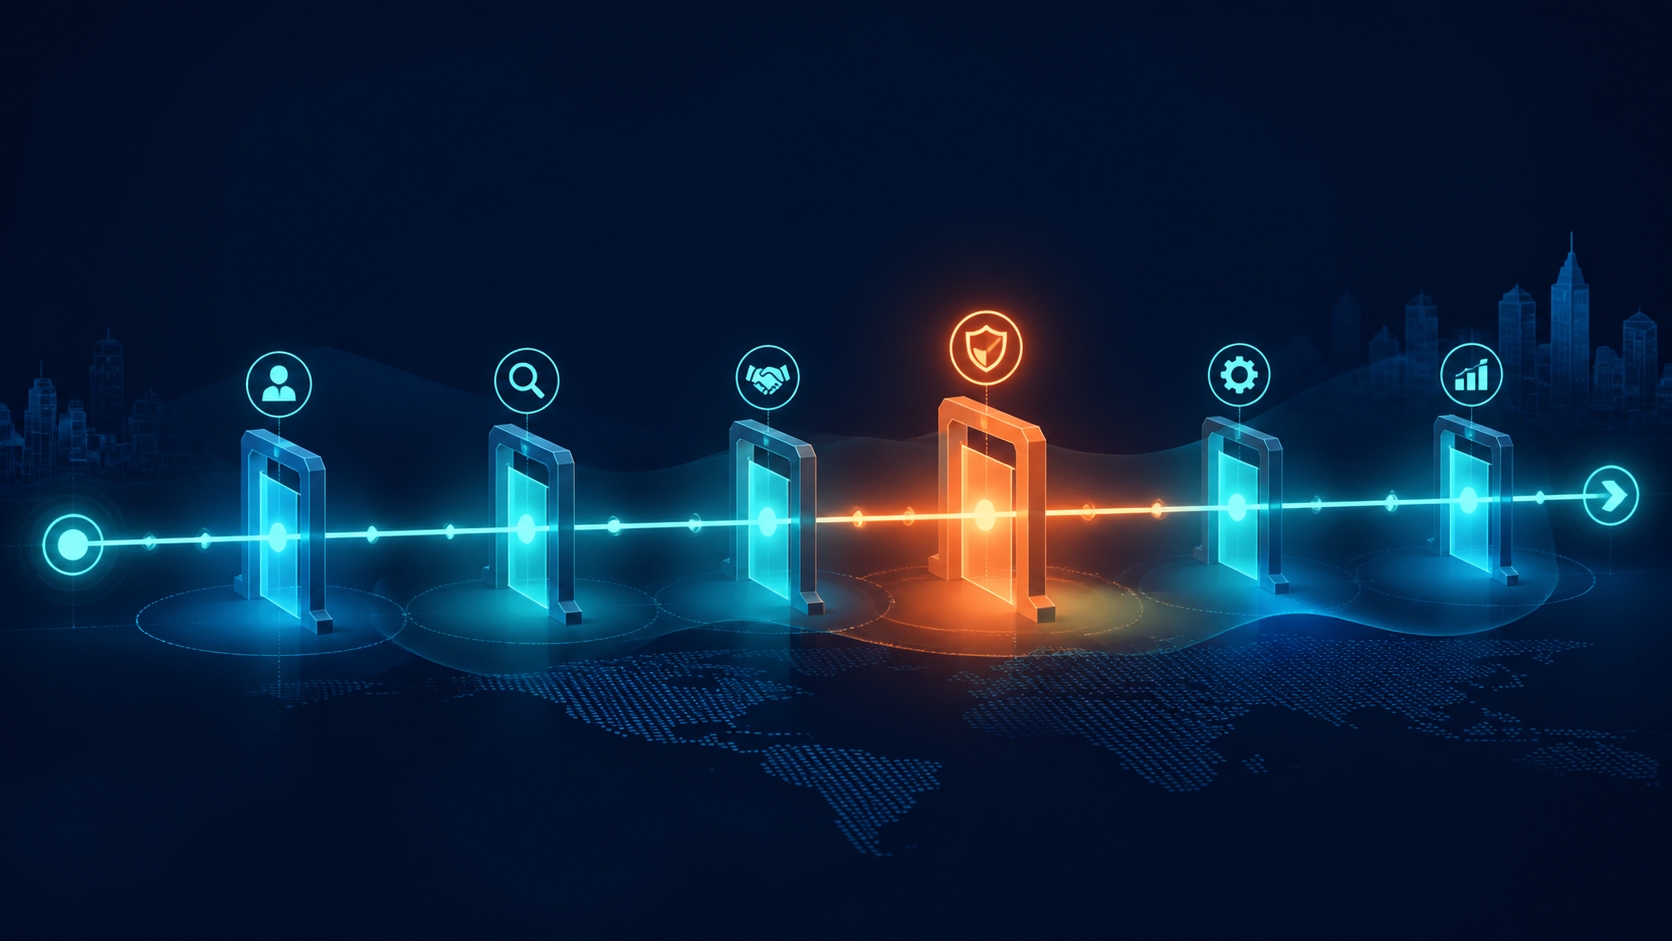
The most valuable verification is not every check, every time. It is the right check, on the right claim or change, before the relevant exposure becomes difficult to reverse.
You cannot fill a tire while the car is moving. That single image carries most of the problem. Every check has a right time, and the right time usually sits before the journey starts, not during it. Yet many risk operations behave as if any check can happen at any moment, so attention spreads evenly and the consequential change arrives too late to prevent.
This is a structure for fixing that. Not a new product, and not a claim that an anomaly proves fraud. A way to organize what we can validate, what we can observe, and what we can control across the relationship lifecycle. Think in analog so we can separate the steps. Operate in digital so we can execute them efficiently.
What fraud prevention is actually for
In commercial risk management, the practical objective is to prevent avoidable loss while enabling legitimate business. Fraud prevention serves that objective, but it is not the whole of it.
A loan, a trade credit balance, or any extension of credit can go unpaid for reasons that have nothing to do with deception. A customer deteriorates financially. An authorized actor acts beyond their authority. An operational error releases the wrong shipment. An external shock breaks a supplier.
Each of these needs different evidence and a different response, even when the financial consequence looks identical on the ledger. Collapsing them into a single label called fraud is how a risk team ends up applying the wrong playbook to the wrong problem.
So the framework separates them. It organizes verification by lifecycle stage, and by what a check is actually trying to establish.
Grounding the framework: understand what is normal
A signal only becomes meaningful against a credible reference point. Before interpreting a change, we need an accurate benchmark: the broader commercial environment, the relevant market, and the individual customer’s operating history.
Normal is not a gut feeling. A broad average is not automatically the right reference for a particular business. An inaccurate benchmark cuts both ways. It can make ordinary variation look suspicious, and it can make a consequential change look routine.
Our intuition is not enough on its own. The last contract we reviewed becomes an anchor. The attractiveness of an opportunity makes us want to accept a reassuring explanation. A memorable example distorts our sense of what is typical when we overlook its population, scope, or limitations.
| Benchmark level | What it grounds | Boundary to preserve |
|---|---|---|
| Macro normal | Broader economic conditions, payment patterns, and external pressures affecting commercial activity. | A population wide pattern supplies context. It does not establish what is normal for every sector or customer. |
| Market specific normal | Expectations for a relevant industry, geography, business model, size, season, and operating cycle. | Choose a defensible comparison group rather than applying an unrelated market’s average. |
| Client specific normal | The customer’s own dated history, usual transaction sequence, payment behavior, destinations, and authorized actors. | A familiar pattern is not proof of legitimacy. Limited or unverified history should not be treated as an assured baseline. |
These levels should inform one another, not compete. A customer’s departure from its own history may be consistent with a market wide shift. A pattern common in the market may still be unusual for that particular customer. Neither comparison alone settles the explanation.
Context matters throughout. What a middle school teacher encounters each day differs from what a bakery owner faces. Their normal rhythms, responsibilities, constraints, and disruptions are different. Commercial benchmarks need the same contextual discipline. An expectation meaningful for one operating model can be misleading for another.
Make the benchmark an explicit part of the decision
- Define the subject, behavior, claim, or condition being compared, and the consequential action the comparison will inform.
- Retain the source, reference population, time period, freshness, coverage, and limitations of the benchmark. Distinguish verified observations from assumptions.
- Consider distributions, ranges, seasonality, and relevant segments rather than relying on a single average. Do not invent universal cutoffs.
- Compare macro, market, and client evidence. Record where they agree, where they diverge, and where they leave uncertainty.
- Refresh the benchmark when conditions or the business model change, without automatically accepting every new pattern as legitimate.
- Where evidence is thin, state that normal is not yet well established, and use a proportionate alternative review path.
The operating sequence is therefore: establish an evidence based expectation, observe the difference, interpret it in context, and choose a targeted response before the relevant exposure becomes difficult to reverse. A departure from normal is a reason to ask a better question. It is not a finding of fraud.
The lifecycle framework
The structure borrows from something we all understand. Prepare before the journey. Monitor while moving. Respond when conditions change. Mitigate harm when disruption occurs. Learn before the next journey. Those layers overlap. They are not a rigid before and after checklist.
The table below maps that structure to commercial risk. The vehicle examples are conceptual illustrations, not technical automotive specifications. The financial controls are proposed design patterns, not validated universal policies.
| Stage | Commercial risk counterpart | Right time and practical response |
|---|---|---|
| Learn before operating | Understand the customer base, normal behavior, products, loss types, and control responsibilities. | Before designing or operating a credit or fulfillment workflow. Refresh when rules or capabilities change. |
| Prepare the operator | Give decision makers and agents clear evidence, permissions, training, and escalation routes. | Before delegated decision making. Revisit when roles or systems change. |
| Prepare the vehicle | Validate baseline business identity, representative authority, submitted claims, and key destinations. | Before onboarding, new credit exposure, or release of goods and funds. |
| Establish visibility | Ensure usable, current, traceable records and transparent workflow status. | Before decisioning and throughout the relationship. Data presence is not the same as data quality. |
| Enable operation | Apply workflow tools, policy rules, scores, and decision support to execute consistent risk decisions. | During routine operation, within defined policy limits. Assistance does not remove accountable oversight. |
| Reduce fatigue and friction | Reuse valid evidence, streamline checks, and present clear next steps to customers and reviewers. | During recurring interactions. Efficiency matters, but convenience cannot substitute for a necessary check. |
| Monitor changing conditions | Track payment behavior, financial condition, identity attributes, account instructions, and exposure. | During the relationship and before relevant new exposure. Baseline validation and monitoring operate in sequence. |
| Respond to disruption | Trigger focused review, step up verification, an exposure limit, or a targeted hold when circumstances materially change. | At the change or warning event, before the consequential action where possible. |
| Limit compounding damage | Stop adding exposure, preserve evidence, and route a deteriorating relationship to appropriate support. | When a condition passes a documented policy boundary or assurance cannot be restored. |
| Mitigate impact | Apply exposure limits, contractual protections, incident response, and recovery arrangements to limit loss severity. | Establish safeguards beforehand. Activate response at the incident. Protection reduces harm without removing the underlying risk. |
| Separate false evidence from changed condition | Distinguish suspected fabricated financial statements from genuine financial deterioration after credit was issued. | Validate evidence before reliance. Monitor financial condition after approval. Both can lead to loss, but they are different problems. |
| Observe anomalies in context | Compare behavior to the business’s history, relevant peers, and expected sequence. Consider combinations of signals. | At onboarding where history exists, in monitoring, and at triggered review. Unusual activity is a lead, not proof of intent. |
| Recheck destinations before shipment | Validate a requested shipping address change against trusted records and confirm requester authority. | Before dispatch. Later rerouting requests need a fresh check. Checking only after dispatch is too late as a primary control. |
| Recheck payment account changes | Validate new bank instructions, the business account relationship, and authority through an established independent channel. | Before activating changed instructions or releasing funds. Account existence is not the same as ownership or authority. |
| Preserve the expert role | Fraud examiners, investigators, legal teams, and recovery specialists establish facts and support appropriate action. | Escalate when evidence or consequences require specialist judgment. Automated flags prioritize work. They do not adjudicate fraud. |
| Restart the cycle deliberately | Refresh expiring evidence, reassess authority, confirm changed attributes, and learn from resolved cases. | At renewal, new material exposure, expiry, significant change, and post incident review. Not every prior approval remains valid indefinitely. |
Two axes: what a check does, and when it belongs
A verification category should not be trapped permanently in either before or after. The four foundations of assurance, collect information, validate evidence, verify identity and authority, and assess anomalies, describe the work. The lifecycle adds the timing.
| Control family | Question answered | Baseline, before exposure | During operation or on change | On disruption or restart |
|---|---|---|---|---|
| Information collection | What is claimed, by whom, and for which action? | Preserve the original application and its purpose. | Capture the exact change request and the actor behind it. | Preserve incident records and corrected claims. |
| Evidence validation | Is the source and evidence sufficiently trustworthy? | Validate documents and key reference records. | Revalidate replacement documents and changed instructions. | Identify invalid evidence and define what must be refreshed. |
| Identity and authority | Is this the right entity, actor, and permitted action? | Establish subject identity and representative authority. | Reconfirm authority for sensitive changes and delegated actions. | Restore authorized access and revoke compromised permissions. |
| Operational transparency | What happened, in what order, and under whose policy? | Define the normal sequence and the approval boundary. | Record request, verification, approval, release, and exceptions. | Reconstruct events and preserve an auditable decision trail. |
| Change detection | What differs from the last known state? | Establish a dated baseline. | Detect material differences without presuming wrongdoing. | Confirm the new state and restart relevant monitoring. |
| Anomaly assessment | Is the difference unusual and consequential against an evidence based expectation? | Establish macro, market specific, and client specific benchmarks, with source and coverage limits. | Interpret magnitude, timing, combinations, and benign explanations against current benchmarks. | Reassess the pattern and the benchmark with investigation findings. |
| Change management | Should this requested change become operational? | Define authority, verification, and approval requirements. | Validate before activating new destinations or permissions. | Correct unauthorized changes and restore a verified state. |
| Credit condition assessment | Has repayment capacity or expected payment behavior changed? | Assess exposure, financial condition, and terms. | Monitor deterioration, performance, and external shocks. | Adjust exposure, collections, restructuring, or recovery approach. |
| Response and loss mitigation | What action limits the specific harm? | Put proportionate safeguards in place. | Step up, limit, or hold the affected action where warranted. | Contain, investigate, recover where feasible, and learn. |
Illustrative signal to action patterns
These are design examples to develop and test. They are not established detection rules, and they are not numerical thresholds.
| Signal or event | Targeted check | Proportionate action while unresolved | Do not conclude |
|---|---|---|---|
| Shipping address change | Corroborate the destination and confirm authority before release or reroute. | Hold the affected dispatch or reroute pending resolution under policy. | A move necessarily means takeover. |
| Payment account change | Independently confirm authority and the intended business account relationship. | Do not activate changed instructions until required assurance is met. | A valid account proves a valid request. |
| Document discrepancy | Check source, alteration indicators, and reconciliations. | Request focused evidence or route to review before relying on it. | Every discrepancy is fabricated evidence. |
| Financial deterioration | Reassess ability to pay and the relevant terms. | Review limits or relationship terms under credit policy. | Inability to pay proves unwillingness or deception. |
| Rapid director or ownership change | Check for legitimate restructuring and confirm who may now act. | Refresh authority and escalate consequential unresolved conflicts. | A leadership change is inherently fraudulent. |
| Dormant to active transition, or thin file | Validate current operations and the specific submitted claims. | Use an alternative evidence path or a proportionate review. | Missing history proves a synthetic business. |
| Unexpected event sequence | Determine whether required steps were skipped or a permitted exception occurred. | Pause the affected action and investigate the sequence. | An ordering anomaly proves intent. |
| Unusual network association | Confirm the relationship and seek independent corroboration. | Refer permitted evidence for specialist review. | A shared address, name, or director establishes guilt by association. |
| Suspected account takeover | Step up through approved channels and verify the requested action. | Restrict the affected change and protect the legitimate account holder. | An authenticated session has unlimited authority. |
What can be managed, and what can only be observed
Clarity about control boundaries is what keeps a framework honest. Some things we design. Some things we watch. Some things we influence through partners. Some things we cannot know from a signal at all.
| Category | Practical boundary | Design implication |
|---|---|---|
| Directly manageable | Our collection requirements, workflow ordering, permissions, exposure, review routing, and release conditions. | Place controls before the action we authorize. |
| Observable but not fully controllable | Counterparty condition, external shocks, registry changes, third party records, and behavioral patterns. | Monitor with freshness and coverage limits. Translate evidence into a proportionate response. |
| Influenceable through partners | Source based verification, secure confirmations, shared evidence standards, and defined response commitments. | Specify the assertion, permitted purpose, independence, latency, fallback, and accountable owner. |
| Not reliably knowable from a signal alone | Intent, ultimate legal liability, every future event, and the counterfactual loss avoided. | State uncertainty. Investigate. Avoid claiming omniscience or guaranteed prevention. |
The minimum record for a useful signal
A signal that cannot be explained later cannot be governed now. This is the contextual record that agents and machine learning systems need in order to support an accountable process.
| Field group | Information to preserve |
|---|---|
| Subject and claim | Business or entity level, actor, the specific claimed fact or requested action, and the relationship being asserted. |
| Timing | Event time, observation time, relevant baseline, and verification freshness and expiry. |
| Evidence | Source, provenance, independence, coverage limits, discrepancies, and evidence references. |
| Context | Macro, market specific, and client specific benchmarks. Reference population and period. Sources, freshness, coverage, and uncertainty. Relevant history and peers, direction of concern, legitimate alternatives, and related signals. |
| Interpretation | Observed change or anomaly, suspected typology if relevant, and a clear separation of expert hypothesis from validated pattern. |
| Decision | Applicable policy, consequential action, targeted check, owner, review deadline, and release or escalation condition. |
| Outcome | Resolved explanation, authorized or unauthorized action, confirmed deception where established, credit deterioration, operational error, unresolved case, and actual loss or recovery where known. |
A fluent explanation is not validated evidence. A model score is not a finding of fraud. Delegated systems must stay within authorized actions and escalate exceptions rather than improvise broader permissions.
The design challenge
Every signal eventually has to route to a decision, and every decision has an owner. The framework above exists to make that routing deliberate rather than accidental.
Three questions keep it honest. What is the last practical point at which this exposure can still be prevented? What evidence do we need at that point, and how fresh must it be? Who owns the action when the evidence does not hold?
Trust makes business possible. Well timed verification makes that trust more durable. The goal is not to inspect everything forever. It is to know what matters next, confirm it before we commit, and respond when the story changes.
Internal Knowledge + External Insights = Competitive Intelligence. That is your Decision Intelligence Framework.
Robert Kirk is Head of Analytics, Global Product at Dun & Bradstreet, supporting AI-driven analytics solutions that generate over $300M in revenue. With 25+ years in data analytics and decision intelligence, Robert focuses on financial risk analytics, commercial credit intelligence, and AI-enabled tools that predict cash flow impact across the full business relationship cycle. As founder of B2B Analytics Insights, he shares insights on financial risk, commercial lending intelligence, procurement analytics, and AI-ready data for C-suite leaders across finance, operations, technology, procurement, and people functions. Every role is responsible for the next profitable decision. That is the lens.